v0.15.0For B2B products · Open source · Runs on your servers
Start with the already built.
Sign-in works. Customers get organizations and projects, or whatever levels your product has, with roles at each level, invites and their own API keys. Your team has an admin console to manage every customer. Every write lands in an audit log, every request has an id you can trace, and the dashboards are already up.
Now add your services, in any language. Every request arrives signed in, checked and traced. That's Plat5.
curl -fsSL https://plat5.com/install.sh | shDocker required.
$ plat5 startrunning
For your customers
For your team
- tasksGo
- billingNode
- + yoursany HTTP server
plat5 start. Keep the defaults or change them; most pieces are optional. You write the dashed boxes./adding-an-endpoint
You write the feature. Plat5 does the rest.
Every endpoint in a B2B product needs the same eight things before the feature. Plat5 does them before the request reaches you. Your handler gets the project id in the path, filters by it and returns JSON. The permission is one line of YAML.
api:
  url: http://api:3000
  scopes:
    project:
      upstream_prefix: /projects/{project.id}
      routes:
        - path: /tasks
          methods:
            GET: { required_permissions: [project:read] }
POST: { required_permissions: [project:write] }Adding POST …/taskswho
Check the token or API keyplat5Find the organization and projectplat5Check the caller's role thereplat5Rate limit itplat5Write the audit recordplat5Attach a request id and traceplat5Format the errorplat5 + starterBuild an admin API for supportplat5
Write the featureyou
/admin-console
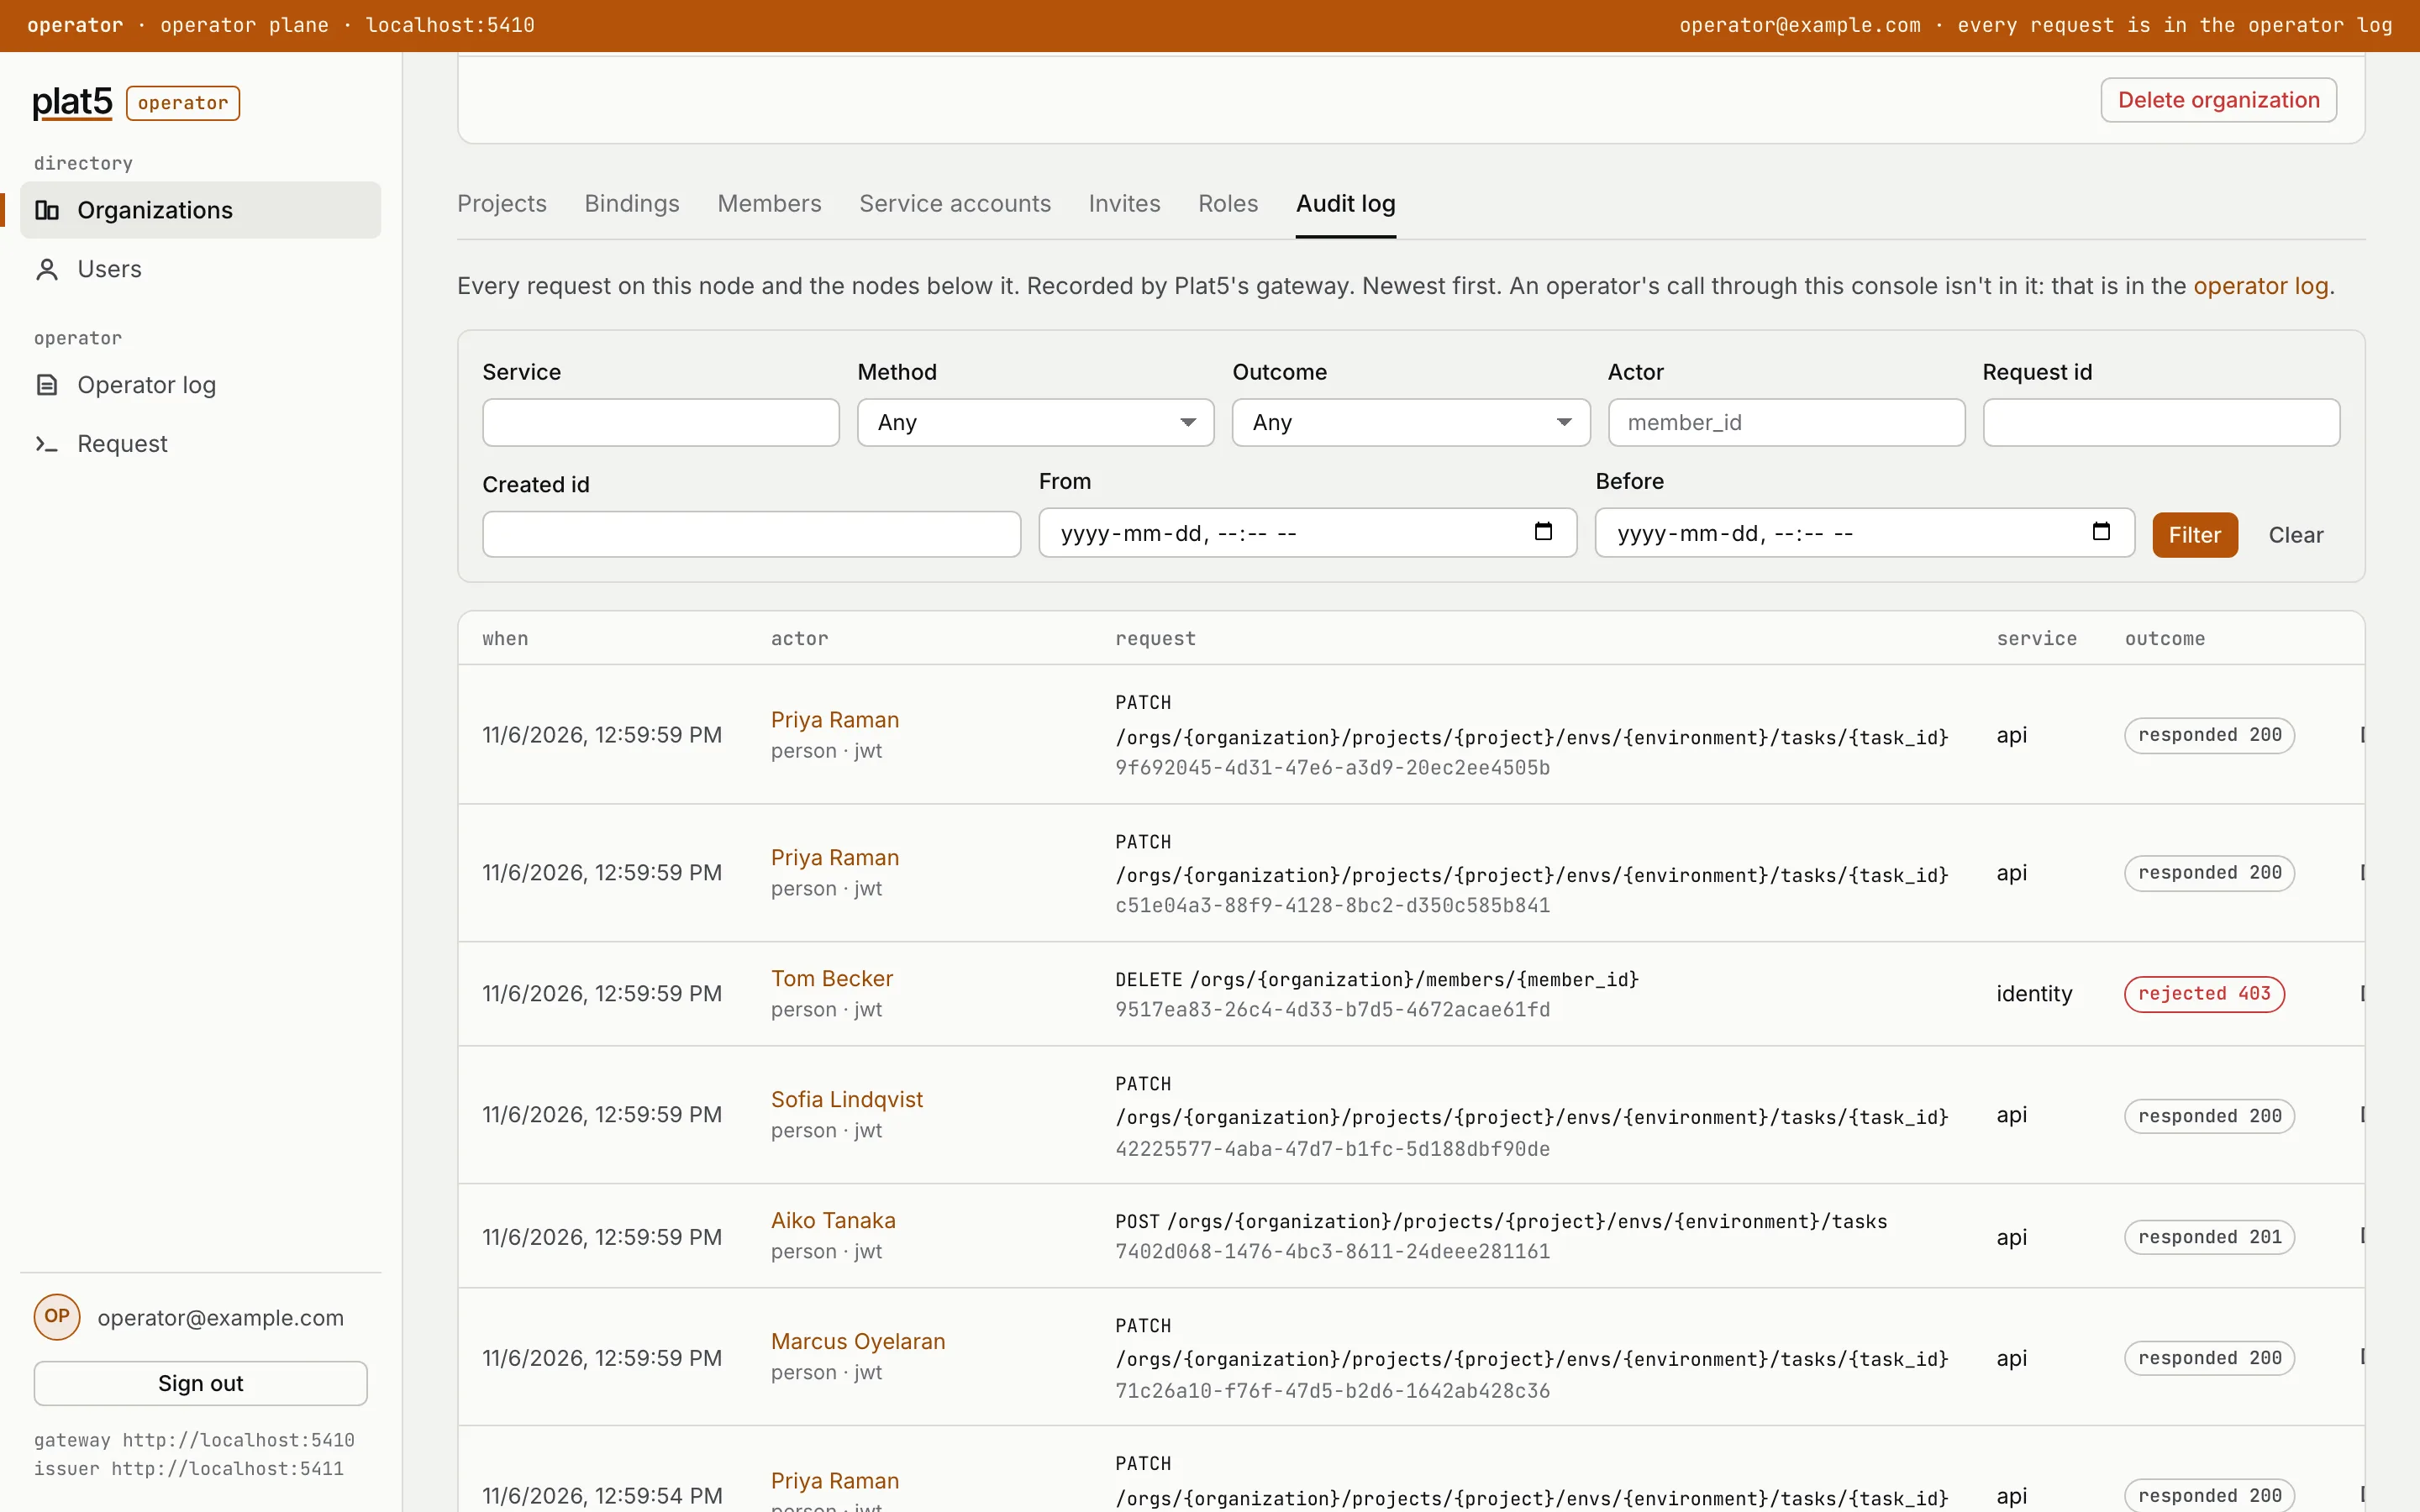
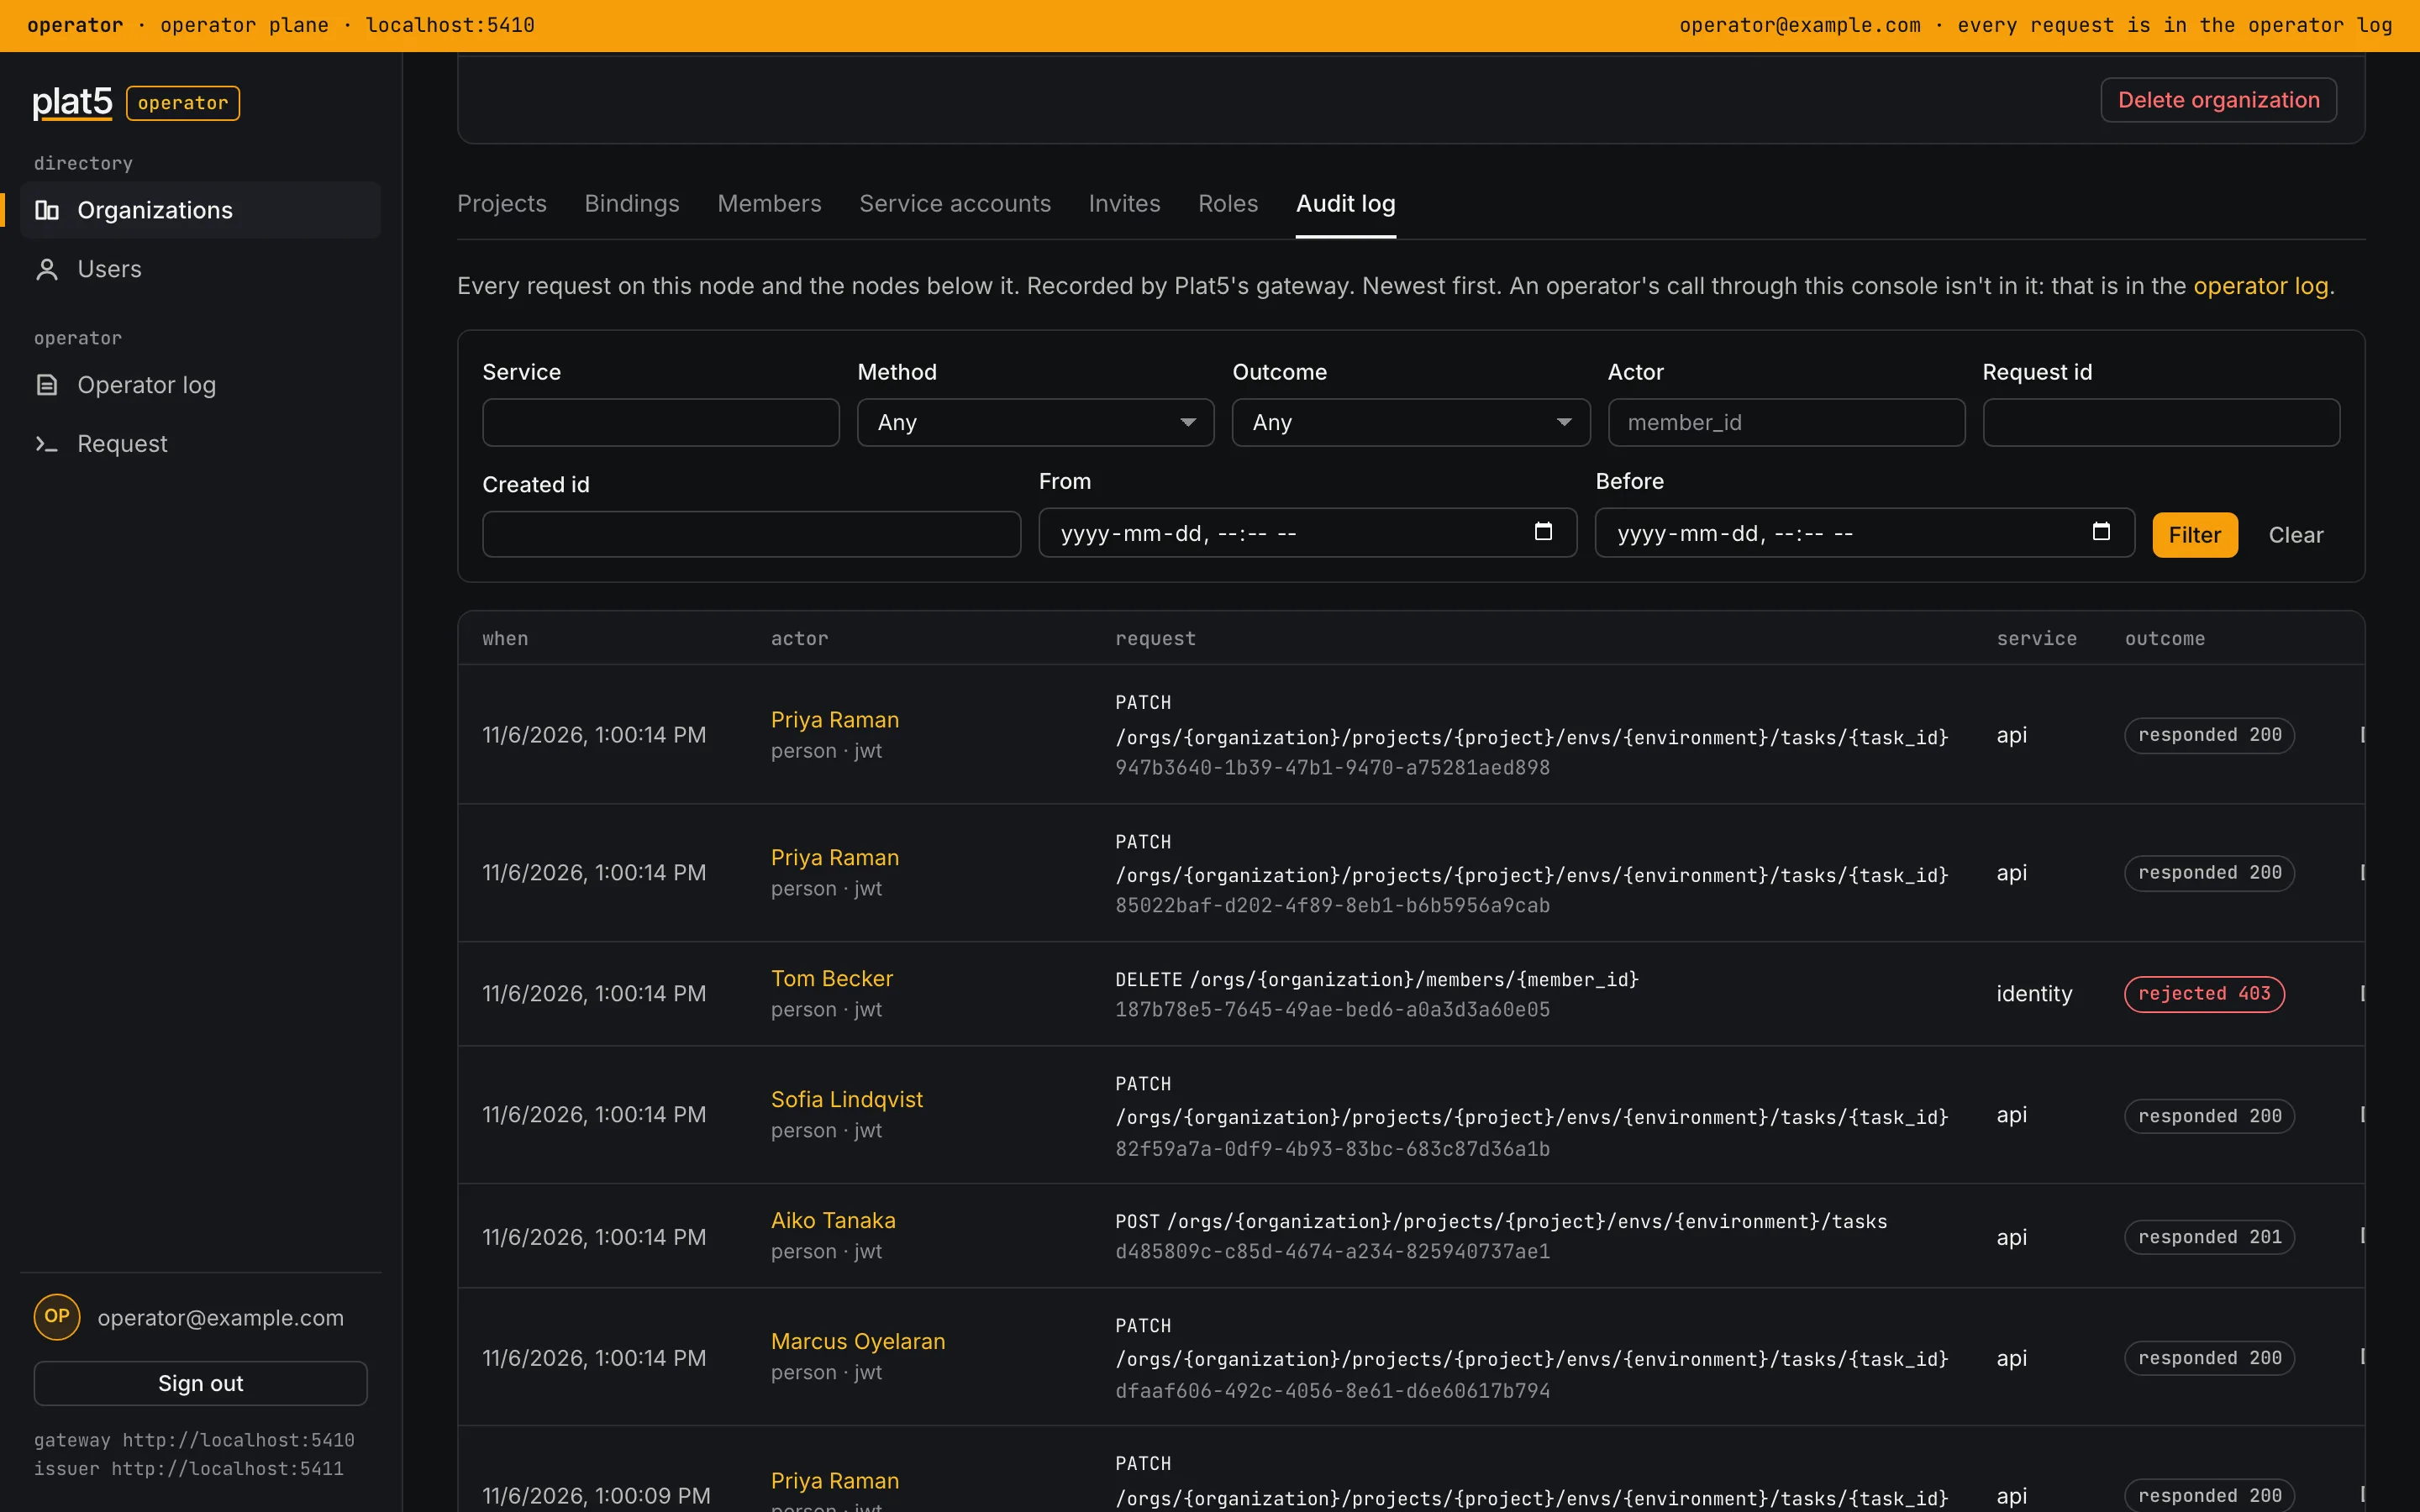
An admin console from day one.
Your company login
Your team signs in with your company's identity provider, never your customers'. No separate accounts to manage.
Every customer
It calls the same service APIs your product does, on any organization or project, so there's no admin API to build.
Every step recorded
Your team's actions go in their own audit log, apart from customers' logs.
Yours to extend
The console is an open-source starter. Fork it and add your own tools.
/coding-agents
Your agent writes the features. Not the auth.
Who is calling, which customer and project it is, whether their role allows it and what gets recorded are decided outside the handler, so generated code can't skip them. Every endpoint follows one pattern, and the line to review is the filter by the id in the path.
/your-call
Sensible defaults. Nothing forced.
Everything works on day one. Keep the defaults, change them, or swap pieces out when you need to.
| Piece | Out of the box | Your call |
|---|---|---|
| Sign-in | Plat5 Auth | Any provider that issues JWT access tokens. Your services don't change. |
| Hierarchy | Organizations, with projects inside | Your own levels, like workspaces or environments, in one file. |
| Roles | Example roles: admin, member, developer, viewer | Rename or replace them, and choose where each can be granted. |
| Audit | Every write, in its customer's log | Choose per route, or turn it off. |
| Rate limits | A default limit on every route | Your own limits per route, shared across a project or an organization, or none. |
| Deletes | Restorable for 30 days | Set the grace period. |
| Telemetry | Grafana on your laptop | Any OTLP collector, or scrape Prometheus. |
| Services | Go, Node and Bun starters | Any HTTP server. |
| Account pages | A starter web app | Rebrand it, fork it, or build your own. |
| Admin console | A starter console for your team | Fork it, or call its gateway directly. |
/best-practice
Best practice, built in.
The defaults a careful platform team would pick, on from the first start.
- Secure by default
- Anything you haven't declared returns 404. Only routes you mark public take anonymous calls.
- Customer isolation
- Access is checked on the organization or project in the path. One you can't reach looks the same as one that doesn't exist.
- Observable by default
- One request id across logs, traces and audit.
- Fail closed
- No audit record, no write.
- Least privilege
- Read-only or limited keys, through a service account with a smaller role.
- Secrets never touch app code
- Credentials are stripped at the edge, and keys are stored hashed.
- Audit by default
- Every write is recorded in its customer's log unless you opt it out.
- Safe changes
- Every config change shows its plan before it applies. Deletes are soft, and restorable.
- Open standards
- OAuth 2.0 JWT access tokens, AuthZEN, OpenTelemetry, Prometheus, W3C Trace Context.
- No lock-in
- Open source, your servers, any identity provider, any language.
/yours
Yours to keep.
Open source
The runtime is Apache-2.0. The CLI, starters, Plat5 Auth and the admin console are MIT.
Your servers, your data
It runs where you run it. Your customers' organizations, members and audit logs live in your Postgres.
Plain HTTP services
No Plat5 SDK in your code. Your services stay ordinary HTTP servers.
Today
Next
Running on your laptop in minutes.
Open source. Runtime Apache-2.0. Everything around it is MIT.
curl -fsSL https://plat5.com/install.sh | shplat5 init my-appcd my-app && plat5 start